@Hevalon: this tuesday, i'm publishing a guide on how to build a complete Agentic system with a harness to support sandboxing, pa…
Summary
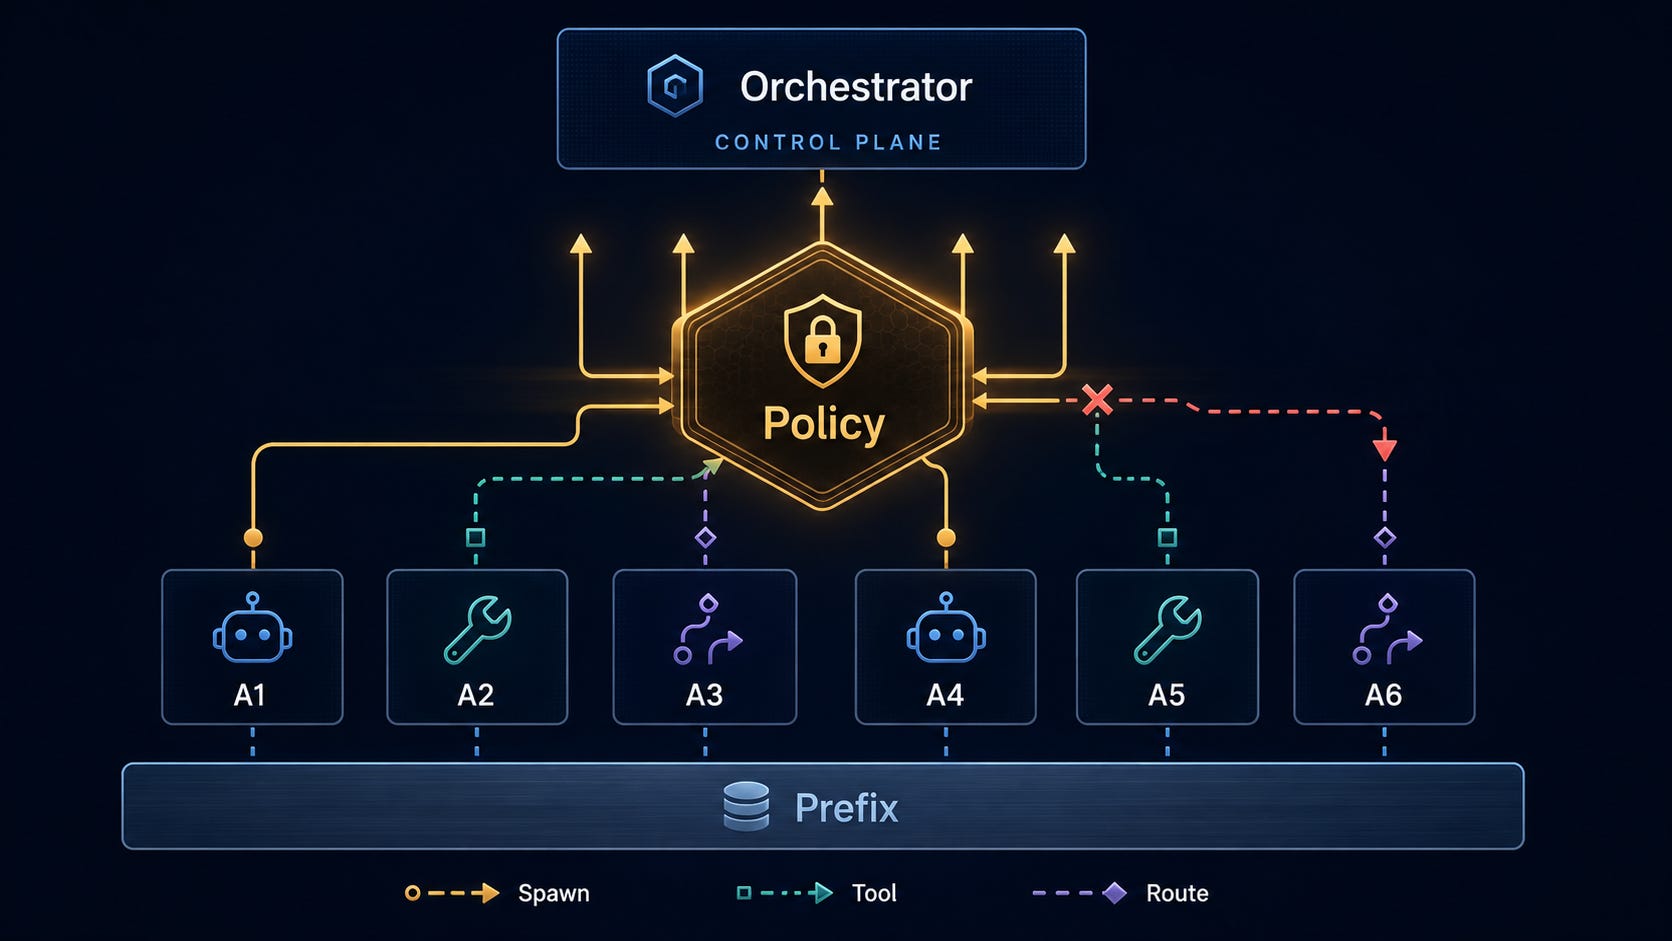
A guide on building a secure agentic system with sandboxing, parallel sub-agents, tool calling with control policies, inference routing, and protection against injection and role escalation attacks, to be published by Evangelos Pappas.
View Cached Full Text
Cached at: 06/08/26, 09:24 AM
this tuesday, i’m publishing a guide on how to build a complete Agentic system with a harness to support sandboxing, parallel sub-agents, tool calling with control policies, inference routing and protection from injection and role escalation attacks. https://hyperautomation.substack.com/p/building-a-secure-agentic-system…
How to Build a Secure Agentic System
Source: https://hyperautomation.substack.com/p/building-a-secure-agentic-system
Building a Secure Agentic System
How to build a secure harness with sub-agents; Real Pi sub-agents, Cedar authorization on every spawn, tool call, and route, with LLMT…
By Evangelos Pappas
Publishes on June 9th, 11:05am. Subscribe now and receive the post in your inbox when it’s live
Available in 1 day, 4 hours, 24 minutes, and 18 seconds
Similar Articles
@kmeanskaran: https://x.com/kmeanskaran/status/2071160257943052683
A detailed guide on building a production-grade agent harness for multi-agent LLM systems, covering components like orchestrator, subagents, skills, backend state management, and context engineering.
@JoshARosen: https://x.com/JoshARosen/status/2105694949438075117
Josh Rosen outlines emerging architectural patterns for the 'agentic security stack' as software development becomes fully agentic — securing the agent worker itself, frontier labs building security agents (OpenAI Codex Security, Claude Code), and vendors embedding security directly into coding-agent loops via MCP, hooks, and skills.
Proper security and maintenance for agentic environments
A developer built Terrarium, an open-source sandboxing solution for running multiple AI agents securely with isolated worlds, reverse-proxy management, and state rollback.
Anthropic on sandboxing agents as their capabilities grow
Anthropic published an engineering writeup on sandboxing AI agents to limit blast radius, discussing permission scoping techniques.
@eyad_khrais: https://x.com/eyad_khrais/status/2069552027382980882
A comprehensive guide to building AI agent harnesses, covering tool execution, context management, state/memory, and guardrails, based on lessons from building Claude Code and other harnesses for enterprise.